
Better Security Starts with Better Visibility
As AI adoption accelerates and hybrid cloud infrastructure grows more complex, security teams face expanding visibility gaps, sophisticated threats, and increasing pressure to respond faster.
Traditional monitoring approaches can miss critical activity across encrypted traffic, east-west communications, and distributed workloads, leaving security tools with incomplete evidence.
The Gigamon Deep Observability Pipeline transforms network traffic into trusted network-derived telemetry, delivering the context security and AI-powered tools need to uncover hidden threats, accelerate investigations, and support faster, more informed response.

AI-POWERED SECURITY OPERATIONS
See how Gigamon Insights turns network telemetry into AI-powered findings and guided actions.
Key Capabilities
Strengthen Threat Detection
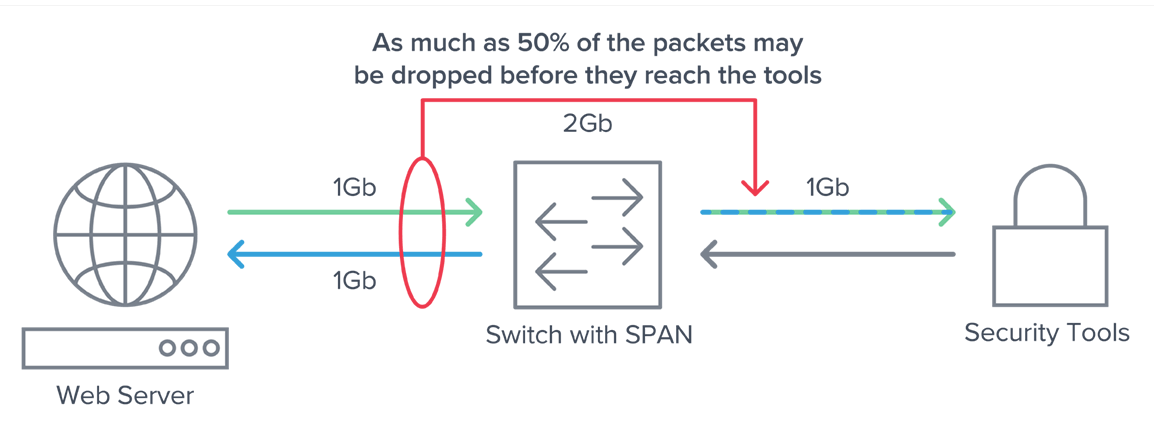
Security tools are only as effective as the network evidence they receive. Fragmented visibility, dropped packets, and incomplete traffic data can limit detection and slow investigations.
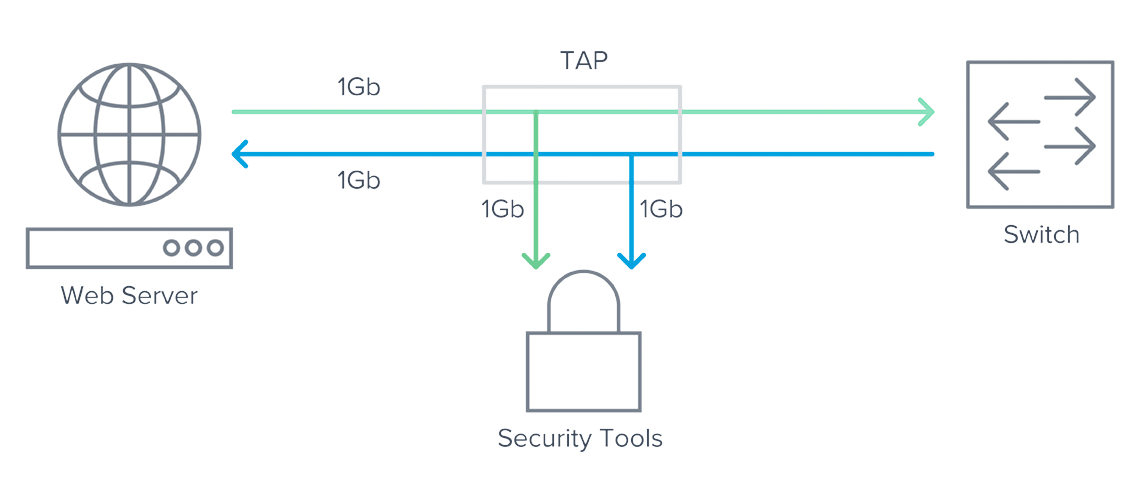
The Gigamon Deep Observability Pipeline aggregates, optimizes, and delivers high-fidelity network traffic across physical, virtual, containerized, and cloud environments.
Gigamon helps security teams:
- Improve detection: Deliver relevant packets, flows, and application metadata to existing security tools.
- Close visibility gaps: Extend monitoring across distributed workloads and east-west communications.
- Optimize tool effectiveness: Reduce unnecessary traffic and improve the quality of telemetry delivered to downstream platforms.
Uncover Threats Hidden in Traffic
Encryption protects sensitive information, but it can also conceal malicious activity from traditional security tools. As encrypted traffic grows across hybrid cloud infrastructure, security teams need ways to investigate potential threats without compromising data protection requirements.
Gigamon helps organizations gain visibility into supported encrypted traffic through two complementary capabilities:
- Gigamon Precryption® technology: Provides visibility into traffic before encryption or after workload decryption, including supported modern encryption protocols.
- GigaSMART® TLS/SSL Decryption: Enables policy-based decryption of supported traffic for inspection by authorized security tools.
Together, these capabilities help security teams investigate suspicious activity, reduce encrypted traffic blind spots, and improve the effectiveness of existing security investments.
Investigate with Richer Context
Security teams need more than traffic volume and connection data to understand suspicious activity. Application-aware context helps analysts identify what is communicating across the network, investigate unexpected behavior, and prioritize potential threats.
Gigamon Application Metadata Intelligence (AMI) extracts rich application and protocol context from observed network traffic, enriching the trusted network-derived telemetry delivered to existing SIEM, NDR, and observability platforms.
Combined with Application Filtering Intelligence and Application Visualization, Gigamon helps organizations:
- Identify application activity: Understand which applications and services are communicating across the network.
- Accelerate investigations: Enrich security workflows with relevant application and protocol context.
- Improve tool efficiency: Direct relevant traffic and metadata to the tools that need them.
From Telemetry to AI-Powered Intelligence
Building on this foundation, Gigamon Insights applies agentic AI to trusted network-derived telemetry to identify hidden threats, surface prioritized findings, and deliver contextual recommendations and guided actions within existing security workflows. This helps security teams accelerate investigations and make more informed response decisions.
Resources
 SOLUTION BRIEF
Gigamon Deep Observability Pipeline
See how trusted network telemetry strengthens security and observability.
 ANALYST REPORT
The Trouble with Visibility Into Cloud Traffic
Explore the challenges of monitoring encrypted traffic across hybrid cloud.
SOLUTION BRIEF
Securing Hybrid Cloud with AI
See how AI and trusted network telemetry strengthen hybrid cloud security.
"A couple of incidents that we had within the last six months we were able to catch quite quickly—within about an hour or so of the time the attacker took ownership of a server. We were able to catch them just in time before any real damage was done. And the reason is we have security tools in place, and Gigamon is feeding all the data into those security tools."

“Enterprises don’t lack AI tools for network operations; they lack trusted data. High-fidelity network telemetry is becoming the foundation for effective AIOps and security, and platforms like Gigamon are emerging as the data layer that ensures AI systems operate on complete, reliable network intelligence.”

"With Gigamon, PT KAI has gained deep observability into risk and threat telemetry, and seamlessly integrated with our security tools, enabling informed decision-making and improved compliance."

“Gigamon [has] helped us move beyond playing whack-a-mole and chasing every vulnerability, toward a more strategic approach to cybersecurity. It gives us the data we need to build network resilience, reduce our attack surface, and make it harder for threat actors to impact our environment.”
Frequently Asked Questions
Security operations helps organizations detect, investigate, and respond to threats before they cause significant harm. It brings together people, processes, and technology to monitor suspicious activity, prioritize alerts, and coordinate incident response.
As environments expand across on-premises infrastructure, multiple clouds, containers, and remote endpoints, effective SecOps helps teams maintain visibility, contain threats, and reduce the impact of security incidents.
SecOps teams often face several connected challenges:
- Alert fatigue: High volumes of low-value or duplicate alerts make it difficult to prioritize genuine threats.
- Tool sprawl: Disconnected security tools can fragment evidence and complicate investigations.
- Incomplete visibility: Gaps in network monitoring can leave relevant activity undetected.
- Limited investigation context: Alerts without sufficient network, application, or endpoint context make it harder to understand what happened and determine the appropriate response.
Staffing and skills shortages can compound these challenges, increasing the time needed to investigate and resolve incidents.
Trusted network-derived telemetry provides independent evidence that helps security teams validate alerts, investigate suspicious activity, and understand the scope of potential threats. By delivering high-fidelity packets, flows, and application metadata to existing security tools, the Gigamon Deep Observability Pipeline adds context that complements logs and endpoint data, helping analysts accelerate root-cause analysis and make more informed response decisions.
This context complements logs and endpoint data, helping teams assess the scope of an incident, investigate its root cause, and make informed response decisions.
The Gigamon Deep Observability Pipeline delivers trusted network-derived telemetry to supported security tools, including SIEM and NDR platforms. By improving the quality, relevance, and context of network evidence, Gigamon helps these tools identify suspicious activity, enrich investigations, and support more informed response decisions. This complementary approach strengthens existing security investments without replacing established workflows or platforms.
By improving visibility and providing trusted network-derived telemetry, Gigamon gives those tools and the analysts using them richer context for investigating threats. It complements the existing security stack, with investigation and response actions carried out through the organization’s security tools and workflows.
Security blind spots are gaps in visibility that prevent security tools and teams from observing relevant activity. They can occur in encrypted communications, East-West traffic between workloads, container-to-container communications, or traffic that is dropped before reaching monitoring tools.
These gaps can allow suspicious activity to go undetected and leave analysts with incomplete evidence during an investigation. Improving visibility helps teams identify activity they might otherwise miss and better understand the scope of potential threats.
Encryption protects the contents of network communications, limiting what security tools can inspect without access to plaintext. Tools may still analyze available connection metadata and traffic patterns, but those signals do not reveal everything within an encrypted session.
Decrypting traffic at scale requires processing capacity, and repeating decryption across multiple tools can increase resource demands. Modern protocols such as TLS 1.3 also limit older passive decryption methods that relied on a server’s private key.
The appropriate visibility approach depends on the environment. Options include supported inline decryption or capturing traffic before encryption or after decryption within supported workloads.
Security operations (SecOps) is the broader practice of bringing together people, processes, and technology to detect, investigate, and respond to cybersecurity threats. A Security Operations Center (SOC) is a dedicated organizational function that performs many of these activities, including monitoring alerts, investigating incidents, and coordinating responses.
A SOC may operate in-house, through an external provider, or through a hybrid arrangement. Organizations can also distribute SecOps responsibilities across teams without maintaining a formal SOC.
Gigamon Insights applies agentic AI to trusted network-derived telemetry to identify hidden threats, surface prioritized findings, and deliver contextual recommendations and guided actions. By integrating with existing security and observability platforms, Gigamon Insights helps security teams accelerate investigations and make more informed response decisions within established security workflows.

Take a Gigamon Tour
See the tech. Touch the tech.
GIGAMON COMMUNITY
VÜE
The Gigamon VÜE Community connects practitioners, partners, and experts to share knowledge, exchange best practices, and access use cases and deployment guides for deep observability and AI-driven operations.